SECURITYFIELD NOTEupdated 5 min read
SSL/TLS handshake basics: how a secure connection starts
Learn the main steps in a TLS handshake, how certificates identify a server, and why people still call it an SSL handshake.
Security / Field note
Learn the TLS 1.3 handshake step by step, read packet captures in Wireshark, inspect OpenSSL output, and troubleshoot common certificate failures.
When you open a secure website, your browser and the website must agree on how to protect their connection. They do this with a TLS handshake. It happens before normal web data, such as a page request, can travel safely between them.
People often say “SSL handshake” or “SSL certificate.” SSL is an older protocol and should not be used today. Modern HTTPS uses TLS, which replaced SSL. This guide explains a common full TLS 1.3 handshake with a server certificate. Other handshakes, such as a resumed session or a client certificate login, can use a different flow.
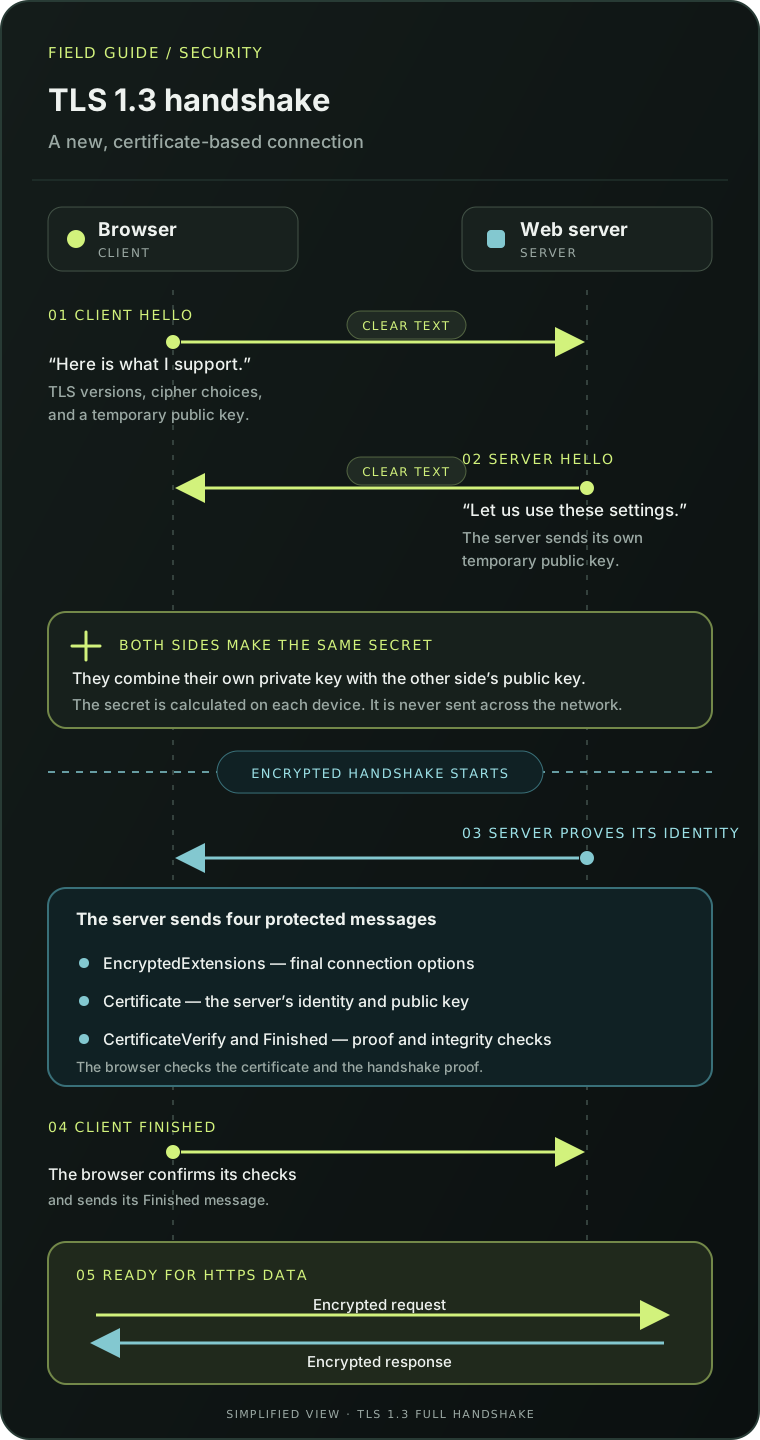
The handshake has three jobs:
The browser does not send the shared secret over the network. Each side calculates it for itself from temporary key information.
ClientHelloThe browser starts with a message called ClientHello. It tells the server which TLS versions and cryptographic options it supports. It also includes a temporary public key share for the key exchange.
The message can include the site name the browser wants to reach. This helps one server choose the correct site when it hosts many websites. In many connections, this name is visible to devices on the network. Encrypted Client Hello (ECH) can protect it when both the browser and server support and use ECH.
Think of this step as the browser saying: “Here are the secure methods I can use. Which one can we both use?”
ServerHelloThe server chooses a supported version and a set of cryptographic options. In this guide, both sides agree on TLS 1.3. The server also sends its own temporary public key share.
Now the browser and server can calculate the same shared secret. The browser combines the server’s public key share with its own temporary private key. The server does the matching calculation with the browser’s public key share and its own temporary private key.
The result is the same on both sides, but the private keys and shared secret do not cross the network. TLS uses this secret to derive keys for the handshake. After ServerHello, the rest of the TLS 1.3 handshake is encrypted.
The server sends a short flight of protected handshake messages. The main messages are:
EncryptedExtensions: extra settings for this connection.Certificate: the server’s certificate, often followed by certificates that link it to a trusted authority.CertificateVerify: a digital signature made with the private key that matches the certificate. It proves that the server controls that key and ties its proof to this handshake.Finished: a check that the handshake messages have not been changed and that the server has the right handshake keys.The certificate contains a public key and information about the server’s identity. It is not the session key, and the browser does not use it to encrypt the page data.
The browser checks whether it can build a trusted path from the server’s certificate to a certificate authority in its trust store. It also checks that the certificate is valid for the requested site name and is within its validity dates. Browser and operating-system policy can add other checks.
The browser then verifies the server’s CertificateVerify signature and Finished message. If these checks fail, the browser stops the connection or shows a security error. A certificate alone is not enough: the browser must also check that the server can prove it holds the matching private key.
For some private business services, the server also asks the browser or user’s device for a certificate. This is called mutual TLS or mTLS. It is optional; most public websites do not ask visitors for a client certificate.
FinishedThe browser sends its own Finished message. This confirms that it has the correct handshake keys and that its view of the handshake matches the server’s view.
After the handshake is complete, the browser and server can exchange application data. For a website, this is usually the HTTPS request and response. TLS protects this data while it moves between the two TLS endpoints.
Wireshark turns captured network packets into a list you can inspect. Each row is a packet frame. A TLS handshake message does not always match one packet: TCP can split a message across packets, or carry more than one message together. Wireshark rebuilds the data stream when it has enough packets.
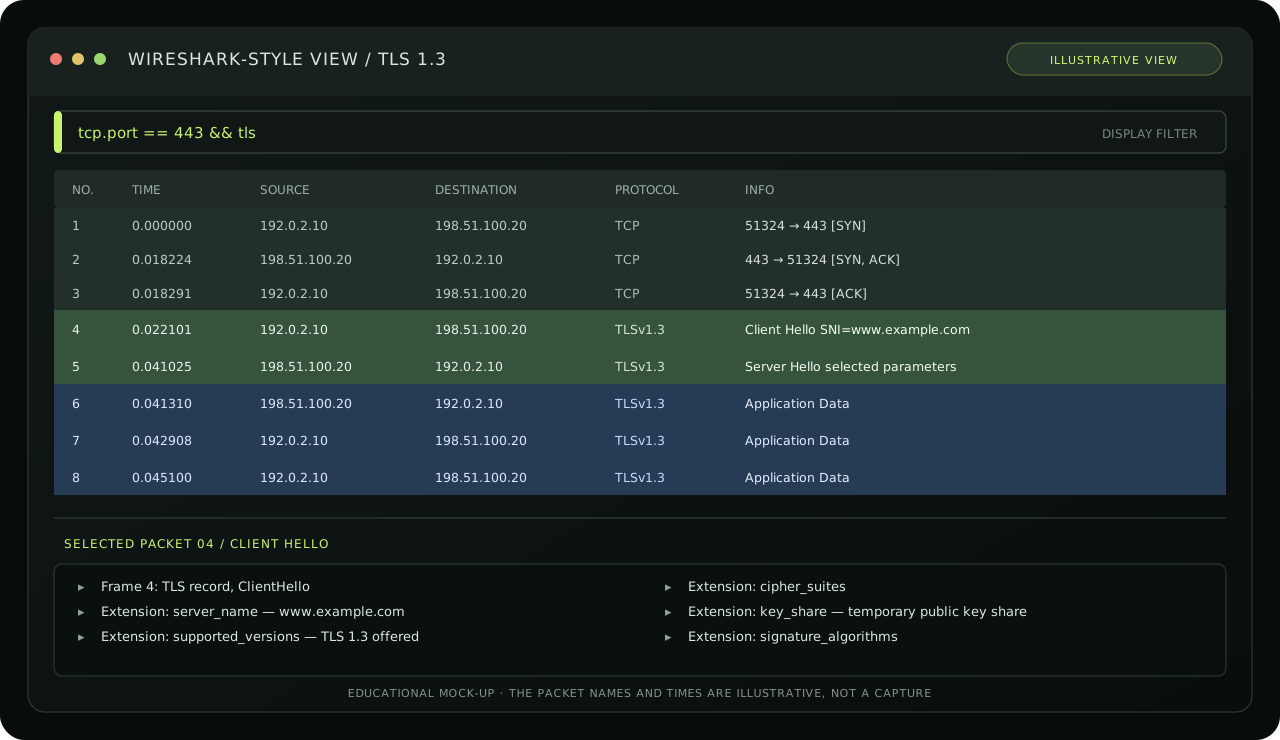
SYN, SYN, ACK, and ACK before TLS starts. This is the transport connection. HTTP/3 uses QUIC over UDP, so this TCP sequence does not apply to HTTP/3.ClientHello shows the client’s offer. Expand it to inspect supported_versions, cipher_suites, key_share, and signature_algorithms. It can also show the requested site name (server_name), unless Encrypted Client Hello (ECH) protects it.ServerHello shows the selection. The server chooses the TLS version and one cipher suite, and responds with key-share information. TLS 1.3 signals the selected version in the supported_versions extension. The legacy_version field can still show 0x0303 for compatibility; that value alone does not mean the connection uses TLS 1.2.ServerHello, TLS 1.3 encrypts handshake messages. Without session secrets, Wireshark may show records as Application Data. That label does not mean the browser has already sent an HTTP request. The encrypted records can contain EncryptedExtensions, the server’s Certificate, CertificateVerify, and Finished, followed by the client’s Finished.Some servers also send a compatibility ChangeCipherSpec record. In TLS 1.3 this can help old network equipment accept the connection; it is not the TLS 1.2 key-change step. Its presence does not make the connection TLS 1.2.
Start a capture on the network interface that carries your test traffic, then open a fresh connection to a test site. In Wireshark, use this display filter to focus on TLS over TCP port 443:
tcp.port == 443 && tlsTo focus on the two hello messages, use:
tls.handshake.type == 1 || tls.handshake.type == 2These are display filters: they narrow the packets shown after capture. If the page creates many connections, check the source and destination addresses and ports so you follow the same client-server conversation. A capture that starts late or misses packets may not show the full handshake.
Wireshark needs the session secrets to decrypt TLS 1.3. For a test connection you control, start a supported browser with TLS key logging enabled so it writes a key log file. In Wireshark, open Preferences → Protocols → TLS and set (Pre)-Master-Secret log filename to that file. Then capture a new connection; a capture made before the key log was available may not be decryptable.
Treat the key log like a password: someone who gets it together with the matching capture may be able to read that session’s protected traffic. Use a test connection, keep the file private, and remove it when you finish. Do not publish key logs or captures that contain private addresses, names, cookies, or other personal data.
Some older Wireshark walkthroughs show ClientKeyExchange, ServerHelloDone, and a certificate that can be read in the capture. That is the older TLS 1.2 flow. For TLS 1.3, use the ClientHello and ServerHello as the visible negotiation, then account for the encrypted handshake messages that follow.
Suppose you open https://shop.example:
shop.example.Someone watching the network cannot read or silently change the protected page data. TLS does not prove that a shop is honest, that a page is free from malware, or that the browser or server has not been compromised. It protects the connection between the TLS endpoints.
| What you see | A possible cause |
|---|---|
| The certificate is expired | The server needs a current certificate, or the device clock is wrong. |
| The name does not match | The certificate does not cover the site name in the URL. |
| The browser or Java does not trust the certificate | The chain is incomplete, or the issuer is missing from the client’s trust store. |
| There is no common TLS version or cipher suite | The client and server have different or too-strict settings. |
| The server asks for a client certificate | The service uses mutual TLS, but the client has no suitable certificate or the server does not trust it. |
| The signature check fails | The server may have the wrong private key or a broken TLS configuration. |
Older guides may show messages such as ClientKeyExchange or ChangeCipherSpec. Those can appear in TLS 1.2 handshakes, but they are not part of the normal full TLS 1.3 flow shown here. TLS 1.3 also does not use the old method where a client encrypts a premaster secret with the server’s certificate key. In the common certificate-based TLS 1.3 handshake, the sides use temporary key shares to calculate a shared secret.
This diagram leaves out session resumption, 0-RTT data, certificate-based client authentication, and transport setup. HTTP/3 uses TLS 1.3 with QUIC; it does not start with a TCP handshake.
This command connects to www.example.com on port 443. The -servername option sends the site name so a server hosting many sites can choose the right certificate and settings. The -tls1_3 option asks for TLS 1.3.
openssl s_client -connect www.example.com:443 -servername www.example.com -tls1_3 -briefHere is the kind of output you may see:
Connecting to 2606:4700:10::6814:179a
CONNECTION ESTABLISHED
Protocol version: TLSv1.3
Ciphersuite: TLS_AES_256_GCM_SHA384
Peer certificate: CN=example.com
Hash used: SHA256
Signature type: ecdsa_secp256r1_sha256
Verification: OK
Negotiated TLS1.3 group: X25519MLKEM768
This is one example. The address, certificate, cipher suite, signature, and key exchange group can change with DNS, server configuration, and OpenSSL version.
Read the main lines like this:
Protocol version: TLSv1.3 means the connection uses TLS 1.3.Ciphersuite: TLS_AES_256_GCM_SHA384 names the algorithm used to protect the data. AES-GCM encrypts and checks the data; SHA-384 is used in TLS key and handshake calculations.Peer certificate: CN=example.com shows part of the certificate’s subject. This line by itself does not confirm that the certificate matches the requested host name.Verification: OK means OpenSSL accepted the certificate chain using its configured trust store. The command above does not ask OpenSSL to check the host name.Negotiated TLS1.3 group: X25519MLKEM768 means the key exchange combined X25519 with ML-KEM-768. This is a hybrid key exchange: it combines a widely used elliptic-curve method with a newer method designed to resist attacks from future quantum computers.To ask OpenSSL to check that the certificate is also valid for the requested host name, add -verify_hostname:
openssl s_client -connect www.example.com:443 -servername www.example.com -verify_hostname www.example.com -tls1_3 -briefIn this sample, the negotiated group is hybrid, but the server’s signature type is ecdsa_secp256r1_sha256. The key exchange and the certificate signature have different jobs. A hybrid key exchange does not mean every part of the handshake uses post-quantum cryptography.
OpenSSL output is useful for learning and troubleshooting, but it does not replace a browser’s full certificate and site checks.
The TLS 1.3 handshake helps the browser and server agree on settings, check the server’s identity, and create shared keys. The certificate helps prove who the server is. Temporary key shares help both sides calculate the secret. After both sides finish the checks, TLS protects the HTTPS data that follows.
Quick answers about certificates, shared keys, packet captures, and common handshake errors. Open a question to see the answer.
8 answersPeople often use “SSL handshake” as a familiar name. SSL is old and unsafe, so modern websites use TLS. When you see this phrase today, it usually means a TLS handshake.
What happens during a TLS handshake?
The client and server agree on TLS settings, create shared secret keys, and check the server’s identity. After they confirm the handshake, they use the keys to protect the data they send.
Does the browser send the shared secret to the server?
No. Each side sends a temporary public key share. The browser and server use their own private values with the other side’s public share to calculate the same secret. The secret itself is not sent across the network.
Does the certificate encrypt the web page?
No. The certificate helps the browser check the server’s identity and verify its proof of the matching private key. TLS derives separate symmetric keys to protect the web data.
Why might Wireshark show “Application Data” before the page loads?
In TLS 1.3, the handshake messages after ServerHello are
encrypted. Without the session secrets, Wireshark may show the encrypted
records as “Application Data,” even when those records still contain
handshake messages such as the certificate and Finished
message.
Does TLS 1.3 use ClientKeyExchange?
No. ClientKeyExchange belongs to older TLS handshakes. TLS
1.3 uses key shares in ClientHello and
ServerHello to create shared keys. A compatibility
ChangeCipherSpec record may still appear, but it does not
mean the connection switched to TLS 1.2.
Common causes include an expired certificate, a certificate for the wrong site name, a certificate chain the client does not trust, different TLS settings on each side, or a missing client certificate when a server requires one.
Usually not from the capture alone. For a test connection you control, Wireshark can use a matching TLS key log file to decrypt it. Keep both the capture and key log private because together they can reveal the session’s traffic.
Continue reading
Learn the main steps in a TLS handshake, how certificates identify a server, and why people still call it an SSL handshake.
Find common TLS handshake problems with OpenSSL, curl, and DNS checks, then learn what each result can tell you.
Reader signal
Your feedback helps shape the next field note and lab.
Views count when this page opens. You can change or remove your vote during this tab session.